If you are going through BSc cyber security course details, the syllabus can look like a long list of unrelated subjects. It is really one idea taught in layers: understand how systems talk, learn to write and read code, then use tools to find and fix weak spots. A BSc cyber security course is generally a three-year, six-semester undergraduate programme, though structure and eligibility vary by university, so check each college’s official prospectus.
Here is what the degree, and the career after it, actually asks of you.
What a BSc Cyber Security Course Usually Covers
Some universities now offer the degree as a four-year honours programme, in line with India’s NEP 2020 framework, with the final year focused on specialisation and real-world work. Subject names and semester order differ between institutions, but the progression usually looks like this:
- Year 1: Foundations. Computer fundamentals, introductory programming (often Python or C), basic mathematics and logic, and an introduction to operating systems and the Linux command line.
- Year 2: Core technical base. Computer networks, database management and SQL, data structures, cryptography basics, and an introduction to ethical hacking and security concepts.
- Year 3: Applied security. Network and web application security, digital forensics, malware fundamentals, cyber laws and IT governance, and hands-on lab work with tools like Nmap, Wireshark and Burp Suite.
- Year 4: Specialisation and industry readiness. Advanced electives such as penetration testing, cloud security, incident response or security operations, plus a major project or dissertation and, in many programmes, an internship.
Whatever the structure, the programming, networking and tools skills in this guide run through every year, so it pays to start practising before your first semester begins. Always check the official prospectus of the college you are considering, since the four-year option and its exit points are not offered everywhere.
Programming Skills: Learn to Read Code Before Breaking It
You do not need to be a software engineer, but you do need to read code and automate small tasks. Attackers write code, and defenders who can’t read it are always a step behind.
Python is the usual starting point. It is readable, and most security scripting, from log parsing to port scanners, is written in it. Aim to write small utilities, such as a script that checks a list of URLs for open ports or flags repeated failed logins in a log file.
SQL matters because SQL injection remains a classic web vulnerability. Once you understand how queries are built, you can see how unsafe input breaks them.
JavaScript and basic HTML help you understand cross-site scripting (XSS) and how browsers handle input.
Bash or PowerShell lets you automate work on Linux and Windows machines.
C or C++ is optional at first. It becomes valuable later if you move toward malware analysis or reverse engineering, since memory-related flaws are easier to grasp once you have seen how low-level code behaves.
A practical tip: don’t collect languages. Get comfortable with Python and SQL first, then add others when a real task demands them.
Networking Skills: The Foundation Everything Sits On
Almost every attack travels across a network, so networking knowledge separates people who run tools from people who understand results. Focus on:
- The OSI and TCP/IP models, and what happens at each layer
- IP addressing, subnetting, DNS, DHCP and routing
- Common protocols: HTTP/HTTPS, FTP, SSH, SMTP, and what makes each one risky or safe
- Firewalls, VPNs, proxies, intrusion detection systems and network segmentation
- Wireless security, including WPA2/WPA3 and how weak configurations are exploited
Try this exercise: install Wireshark, capture your own traffic while loading a website, and trace the DNS lookup, the TCP handshake and the TLS negotiation. One hour of that teaches more than a chapter of theory.
Operating Systems and Core Security Concepts
Get comfortable with the Linux command line. Most security tools run on Linux, and distributions such as Kali Linux are built around them. Also learn how Windows handles users, permissions, the registry and logs, because most corporate environments run on it.
Alongside that, learn the core security ideas: the CIA triad (confidentiality, integrity, availability), encryption and hashing, authentication and access control, and common attack types like phishing, ransomware and privilege escalation.
Tools Every Beginner Should Know
Tools are easier to learn once the fundamentals are in place. Start with these:
| Purpose | Tool examples | What it teaches you |
| Network scanning | Nmap | How to discover hosts, open ports and services |
| Packet analysis | Wireshark | How protocols behave on the wire |
| Web testing | Burp Suite, OWASP ZAP | How web apps handle input and sessions |
| Exploitation frameworks | Metasploit | How known vulnerabilities are tested in a lab |
| Password auditing | John the Ripper, Hashcat | Why weak passwords fail |
| Monitoring | Splunk, Security Onion, ELK stack | How defenders detect suspicious activity |
| Forensics | Autopsy | How evidence is recovered from storage |
Practise only on systems you own or are explicitly authorised to test. Beginner-friendly legal options include deliberately vulnerable practice labs and capture-the-flag (CTF) platforms such as TryHackMe and Hack The Box.
Soft Skills That Quietly Decide Careers
Technical ability gets you an interview. These skills help you keep the job and move up:
- Analytical thinking: security work is mostly investigation
- Clear writing: incident reports and risk summaries must be understood by non-technical managers
- Curiosity and persistence: new vulnerabilities appear constantly, and learning never stops
- Ethics: you will handle sensitive data and access, so integrity is part of the job
Career Paths and Certifications to Consider
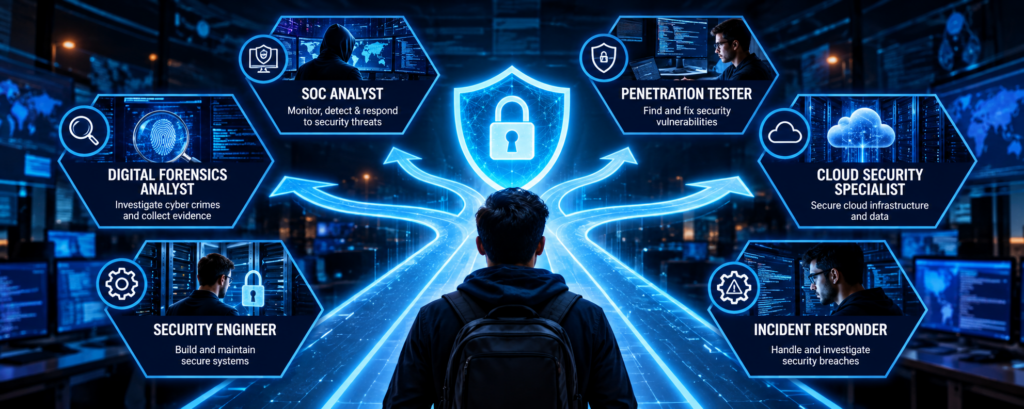
After a BSc, common entry roles include SOC analyst, junior penetration tester, vulnerability analyst and security support engineer. Certifications often discussed for beginners include CompTIA Security+, CEH and, later, OSCP. Requirements and exam details change, so check each provider’s official site before committing money.
Studying Cyber Security in Kolkata
Students from across the city and its suburbs, whether from Baguiati, Barasat, Sonarpur, Serampore, Chandannagar or Berhampore, or from central areas like Sealdah, Chowringhee, Jodhpur Park and New Alipore, often compare colleges and training institutes. When you do, ask these questions:
- Does the syllabus include hands-on lab work, or only theory?
- Are there CTF practice sessions, projects or internship support?
- Is the course content updated regularly?
- Can you see sample material or speak to current students?
Choose the option that gives you the most real practice time, not just the most impressive brochure.
Frequently Asked Questions
1. What is the duration and eligibility for a BSc cyber security course?
It is typically three years, with eligibility usually based on completing 10+2. Some universities prefer science or mathematics subjects, others accept any stream. Always confirm with the specific institution.
2. Do I need coding skills before joining?
No. Most programmes start from the basics. But practising Python before you begin gives you a real head start.
3. Is a BSc cyber security course better than a general BSc in computer science?
Neither is better in every case. Computer science is broader. Cyber security specialises earlier, which helps if you already know security is your goal.
4. Which programming language should I learn first?
Python, followed by SQL. Together they cover automation, data handling and understanding injection flaws.
5. Can I learn the tools without a degree?
You can learn the tools through free labs and CTFs. A degree adds structured fundamentals and is often preferred by employers, especially for entry-level roles.
6. How long does it take to become job-ready?
It depends on practice, not just time. Students who build labs, join CTFs and document projects usually present stronger portfolios than those who only attend classes.
7. Is mathematics important?
Basic logic and discrete maths help, especially for cryptography. You do not need advanced maths for most entry roles.
Conclusion
Your BSc cyber security course details point to one path: learn how networks work, write enough code to automate and understand attacks, and then use tools with purpose. Start with Python, Wireshark and Linux, practise in legal labs, and let curiosity guide you deeper. If you are also exploring creative technology fields alongside security, you can look at Moople Institute’s animation course to see what else is on offer.
Farhat Jabeen is passionate about documenting the student enrollment journey in the fields of technology, design, and digital media. Through her writing, she shares practical guidance, industry insights, and real-world learning experiences that help aspiring students confidently navigate their path toward creative and technology-driven careers. Her goal is to empower learners with the knowledge they need to choose the right educational journey.